
MIL-STD-810H Tested
Tested for durability and backed by one of the industry’s lowest failure rates, ready for the rigors of mission-critical use.
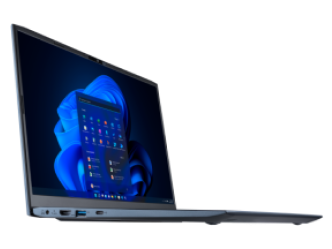
Satellite Pro laptops merge cutting-edge tech with reliability, adaptability and value.
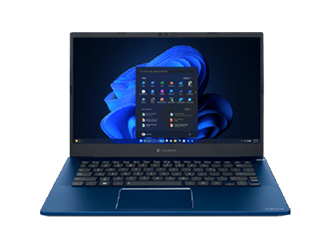
Tecra laptops boast ergonomic designs, premium features, and connectivity options.
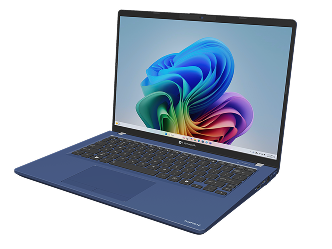
Portégé laptops and 2-in-1s are built using premium materials and boast high-end features.
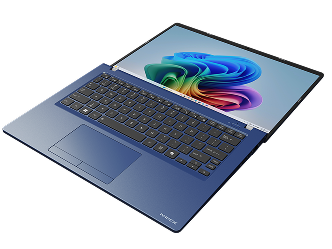
The Portégé® Z40L is a lightweight PC under 1kg with an Intel® Core™ processor.
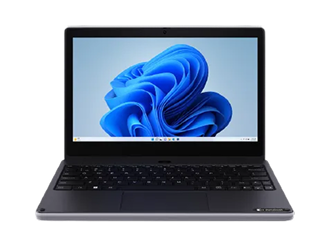
Unlock learning with the Dynabook E11. Durable solutions for remote education.
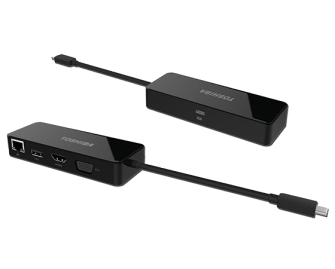
Streamline your workflow and work seamlessly with Dynabook laptops and a wide range of Windows PCs.
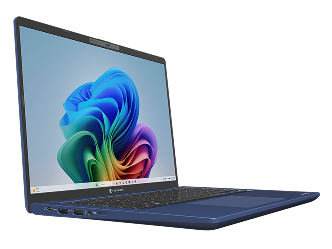
Powerful, customizable laptops built for secure, productive work.
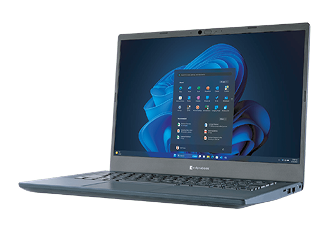
Flexible laptops that help small businesses work smarter and grow.
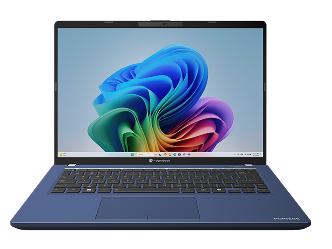
Durable laptops designed to keep learning moving.
Secure, reliable laptops built for better care and productivity.
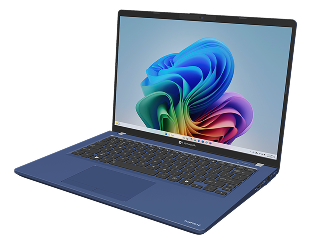
Dependable laptops built for secure government work.
Whether deployed in the field, supporting, operating in healthcare facilities, or working from secure locations, our federally compliant laptops are purpose-built to meet the complex demands and stringent security needs of those who serve our nation.
Tested for durability and backed by one of the industry’s lowest failure rates, ready for the rigors of mission-critical use.

Hardened with Secured-Core architecture to support zero-trust strategies and protect the most sensitive government data.

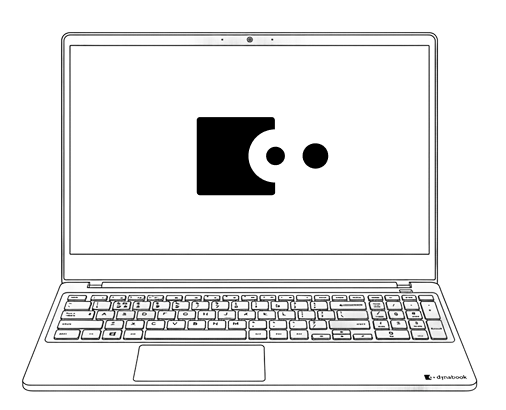
Dynabook’s Windows 11 Secured-core PC laptops integrate advanced security with robust hardware and software defenses. They provide a shield against cyber threats, employing specialized protections to safeguard critical data and uphold business integrity.


Hardware Root of Trust
This involves secure hardware components that establish a foundation of trust, ensuring the integrity of the system’s boot process and safeguarding against firmware-level attacks.
Proprietary BIOS
Nearly eliminates the possibility of BIOS-level attacks and safeguards the foundational firmware of our laptops. No other laptop brand does this.
Firmware Protection
Secured-core PCs implement secure firmware with measures to prevent unauthorized modifications or tampering, ensuring a secure boot process and protecting against firmware-based attacks.
Trusted Platform Module (TPM)
TPM is a hardware security feature for secure storage of cryptographic keys and sensitive information, enhancing protection against attacks.
Enhanced Operating System Security
Secured-core PCs run Windows 11 Pro with built-in security enhancements and protections, reducing the attack surface and mitigating the risk of exploits.
Isolation and Virtualization Technologies
These technologies create secure enclaves or isolated environments within the system to protect critical processes and sensitive data from potential threats.
Hardware Root of Trust
This involves secure hardware components that establish a foundation of trust, ensuring the integrity of the system’s boot process and safeguarding against firmware-level attacks.
Proprietary BIOS
Nearly eliminates the possibility of BIOS-level attacks and safeguards the foundational firmware of our laptops. No other laptop brand does this.
Firmware Protection
Secured-core PCs implement secure firmware with measures to prevent unauthorized modifications or tampering, ensuring a secure boot process and protecting against firmware-based attacks.
Trusted Platform Module (TPM)
TPM is a hardware security feature for secure storage of cryptographic keys and sensitive information, enhancing protection against attacks.
Enhanced Operating System Security
Secured-core PCs run Windows 11 Pro with built-in security enhancements and protections, reducing the attack surface and mitigating the risk of exploits.
Isolation and Virtualization Technologies
These technologies create secure enclaves or isolated environments within the system to protect critical processes and sensitive data from potential threats.